Script Kiddies
Metasploit, Red Lion, and the jump that goes the wrong way
You're viewing revision R0 from Nov 17, 2026. See the current version.
There is a word hackers use for people who hack without knowing how. Script kiddies. They download a tool, pick an exploit off a menu, point it at an address, and press go. When it works they feel like a wizard. When it doesn't, they have no idea why, because they never knew what it was doing in the first place.
The tool most of them reach for starts with an M. Metasploit is a free framework packed with ready made exploits. It was built for penetration testers, the people companies pay to break in on purpose so the holes get fixed. In a professional's hands it saves weeks. In a kid's hands it is a vending machine. Same buttons, very different understanding.
Where I learned the other half
Somewhere around 2016 to 2018, while I was doing relay and protection and NERC CIP work at ComEd, they sent us through security training with Red Lion, a firm that pulls people out of the hacker community to teach utilities and big companies how attacks actually work. The point wasn't to turn engineers into attackers. It was to show us what the button on the vending machine is really doing.
The lesson that stuck was code injection. A program is just a list of instructions sitting in memory, and the processor walks down that list. Every so often it hits a branch or a jump, an instruction that says go over there next. Normally those addresses are fixed by the person who wrote the program. But if the program takes input from the outside and doesn't check how big it is, that input can spill past where it was supposed to go and overwrite the spot that says where to jump. Now the processor isn't following the programmer's directions anymore. It is following yours.
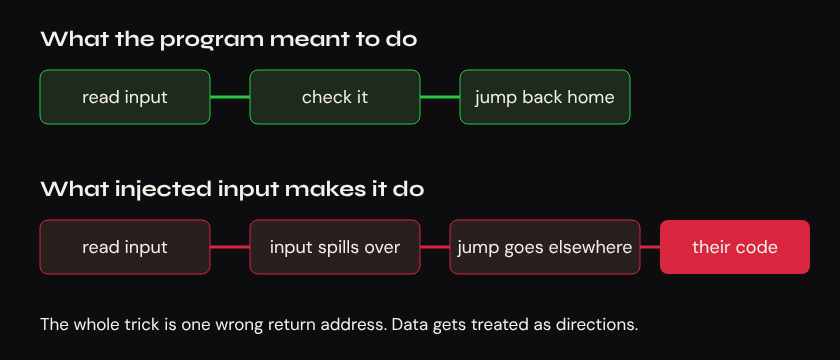
That is the whole magic. Data gets treated as directions. Once you see it at the assembly level, a lot of mystery falls away. You stop thinking of hacking as genius and start seeing it as sloppy bookkeeping somebody else left behind.
Why the kiddies still matter
Who is this post for? Nobody special. Anyone curious about how the tech actually works. But here is the uncomfortable part. Script kiddies don't need to understand anything for their tools to work. The understanding has already been packaged by someone else. The more a target runs the same common software everyone else runs, the more a menu of canned exploits applies to it.
That is why the systems that keep the lights on worry me most. A lot of them sit on the most common, most studied, most packaged operating system on earth. That is its own post, and it is the next one.
Inspired by Happy, written by Claude.
NextNot on WindowsRevision history (R0 current)
| Rev | Date | What changed | Page |
|---|---|---|---|
| R0 | Nov 17, 2026 | First published. | view |